SICPA supplies governments with security inks, product authentication and traceability solutions. It now faces allegations concerning its own information security. In its official materials, the company says it serves governments, central banks and high-security printers. SICPA’s activities
The tip received by The Ledgers included screenshots of correspondence between SICPA employees. The images contain warnings about issues identified through the company’s own audits and security tests.
A “high risk” warning over access rights
An email about the periodic review of access rights states:
“It was reported that the following finding from the audit conducted in 2021 remains open.”
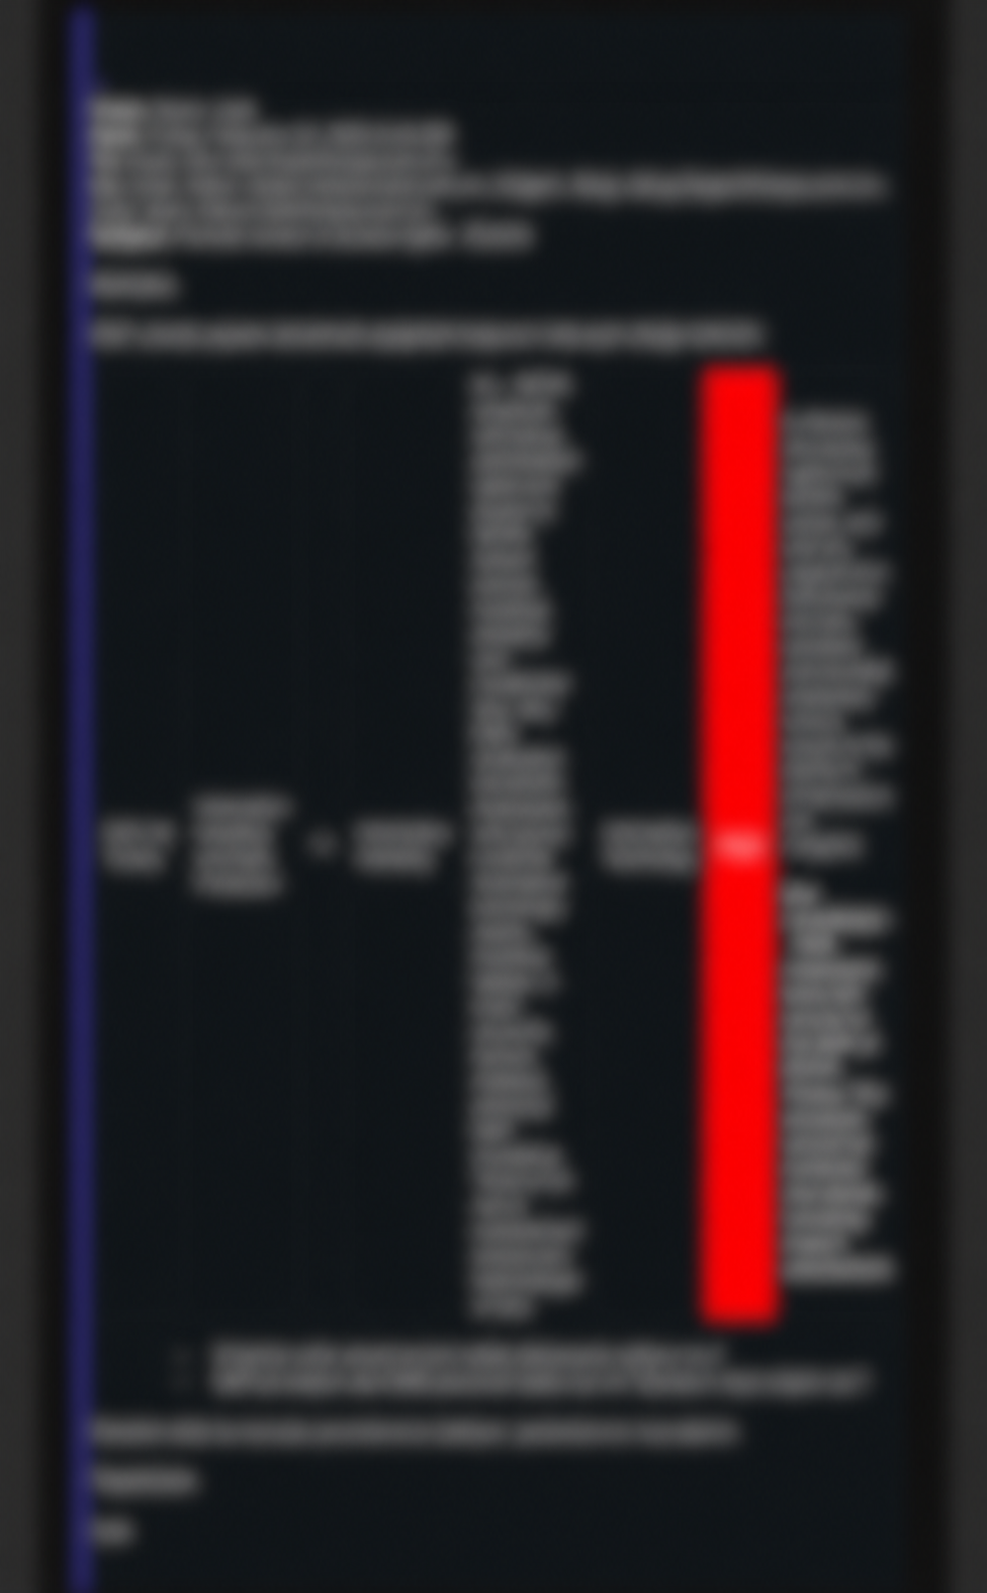
The audit table in the message states that a former SICPA employee retained administrator rights and access to shared servers containing sensitive files. It also addresses access by personnel referred to as “DNS” to the company’s IT resources, including laptops, email accounts, software and the local SAP system.
The table classifies the risk as “High”. The same entry states that the finding has not been remediated, noting that DNS personnel still have access to SICPA Türkiye’s SAP system. It calls for a detailed review of access and an impact assessment.
The message goes on to ask whether access rights are checked and documented annually, and what information DNS personnel with SAP access can reach. The correspondence therefore highlights both an identified risk and a need for clarification about how access rights are monitored.
Protecting sensitive files
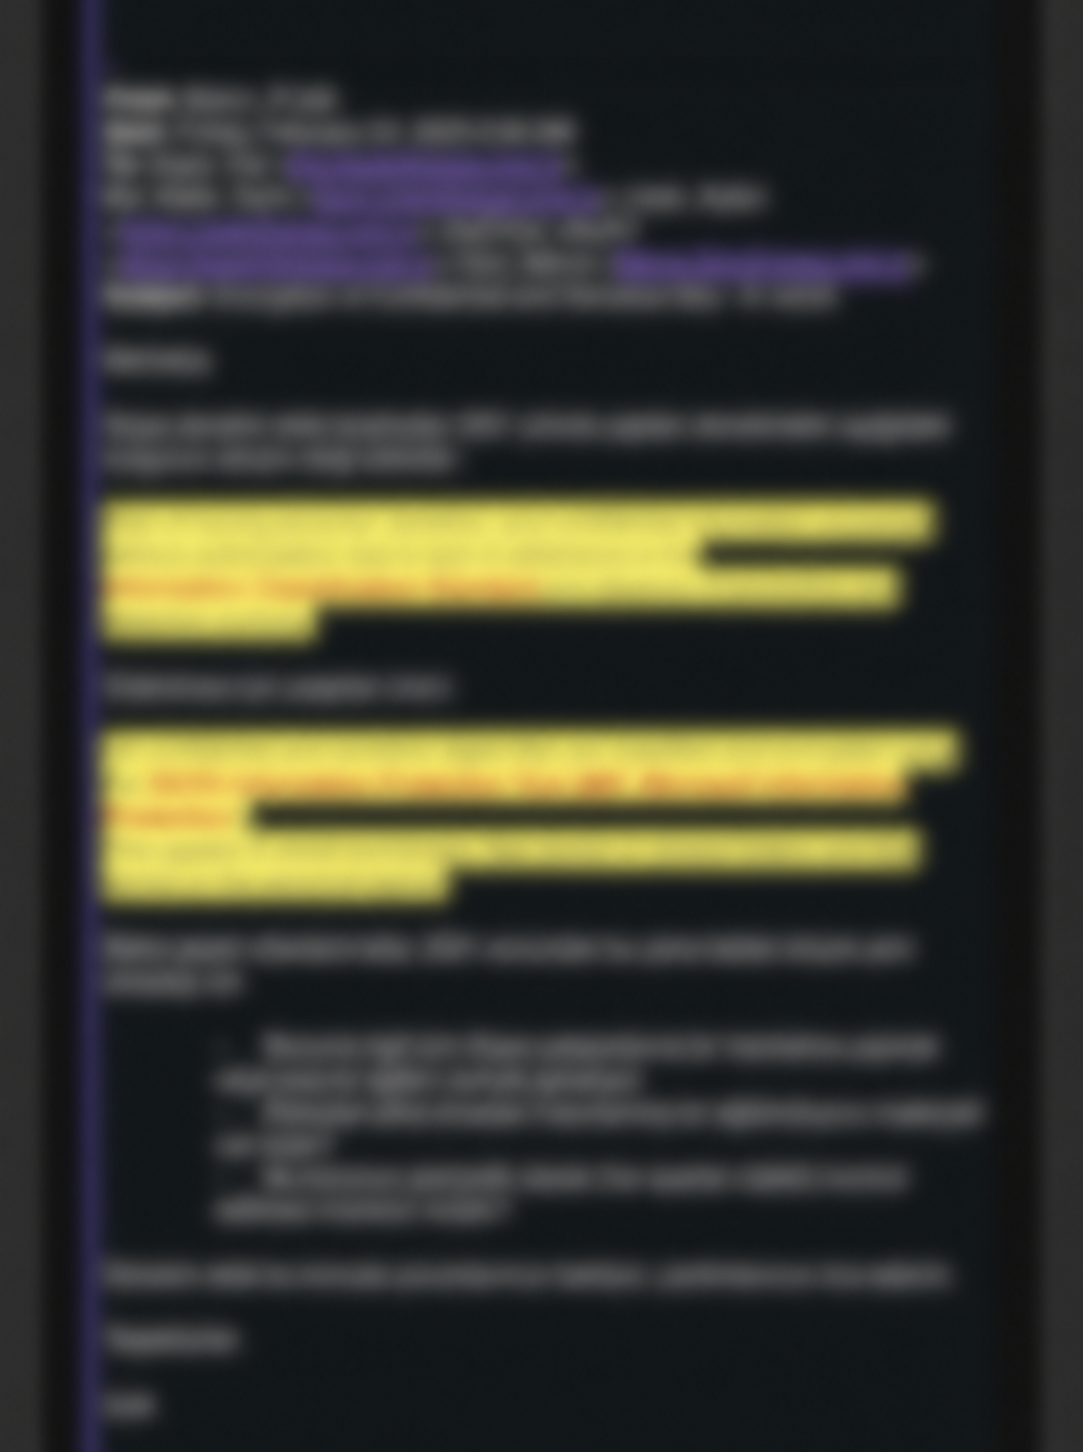
Another email appearing to have been sent on the same day states that an audit finding concerning the protection of personal, sensitive and confidential information remains unresolved. The cited finding points to a risk of unauthorized access arising from non-compliance with the information classification standard and the absence of preventive or detective controls.
The recommended measure is to classify and encrypt confidential and sensitive digital files using the company’s information-protection tool. The stated scope includes email exchanges, files in shared folders and documents on employees’ laptops. Reminders or brief training for employees, along with periodic checks on implementation, are also proposed.
Around 1,800 accounts in a password test
A separate exchange dated 23 February 2023 states that the company’s security unit conducted a password-cracking exercise in November 2022. The same message says that a previous exercise in 2021 cracked passwords for around 1,800 accounts at SICPA. It requests an immediate password change for a user whose password was reportedly cracked in the latest test.
The reference to 1,800 accounts appears in the context of the company’s own security testing; the correspondence does not say that all of these accounts belonged to the Türkiye operation. Conducting a security test does not itself establish a breach. The key issue for this report is which measures were implemented after the deficiencies were identified in tests and audits, and when.
Other publicly disclosed incidents in the sector
The responsibility of security-technology providers to protect their own systems has also been debated following other publicly disclosed incidents. Although these companies operate in different fields and their incidents must be assessed separately from the allegations concerning SICPA, they illustrate risks facing the sector:
| Company | Year | Publicly disclosed incident |
|---|---|---|
| Entrust | 2022 | The digital identity and data-security company confirmed unauthorized access to systems used for its internal operations and the taking of data. Report citing the company’s statement |
| RSA Security | 2011 | The company said information had been extracted from its systems, some of it relating to its SecurID authentication products. RSA’s statement |
| FireEye | 2020 | It disclosed the theft of tools used for security testing and attributed the attack to a state-sponsored actor. FireEye’s statement |
| Okta | 2023 | It said a report containing the names and email addresses of support-system users was taken in a breach of its customer-support system. Okta’s update |
| Verkada | 2021 | Customer video data was accessed in a breach of its camera platform. The initial figure of 95 customers was revised to 97 in a subsequent incident report. Verkada’s incident report |
| G4S | 2022 | Its Australian operation said that an unauthorized third party published some information online after a cyber incident on 5 July. G4S’s notice |
| Thales | 2022 | After LockBit published data relating to the company, Thales said it had detected no intrusion into its own IT systems. It identified a partner’s account on a collaboration portal as one of the sources. Thales’s statement of 11 November 2022 |
Response and current status
The available material does not include a company response to this specific correspondence. The original emails, relevant audit reports, records showing the closure of findings and SICPA’s response will be central to establishing the scope of the allegations.
The supplied screenshots bear the dates 23–24 February 2023. By themselves, these images do not establish the status of the findings after those dates.